
For the complete documentation index, see llms.txt.
Screenshots use fictional example data. The names in your organization will differ.
How workspaces organize your data
A workspace is a separate body of mission work inside your organization. Give each workspace a recognizable name. You can keep several independent sets of mission data and member access without creating another organization.What is separate, and what is shared?
If you represent the same physical spacecraft in two workspaces, those are
independent records, not a single shared spacecraft. Editing one does not
update the other. Creating a workspace does not copy any spacecraft or other data
into it.
When should I create another workspace?
Create another workspace when you need a separate set of mission inputs, results, activity or members. You do not need one workspace per satellite: a workspace can contain a whole constellation. Keep spacecraft together when you want to work on them together; split workspaces when the work needs its own data or access boundary. A different team alone does not require another workspace if it works on the same data. For example, the fictional organization Example Space could use:
These are organizational choices, not required categories. Start with your
existing workspaces if you do not need another boundary.
The permanent default versus your remembered selection
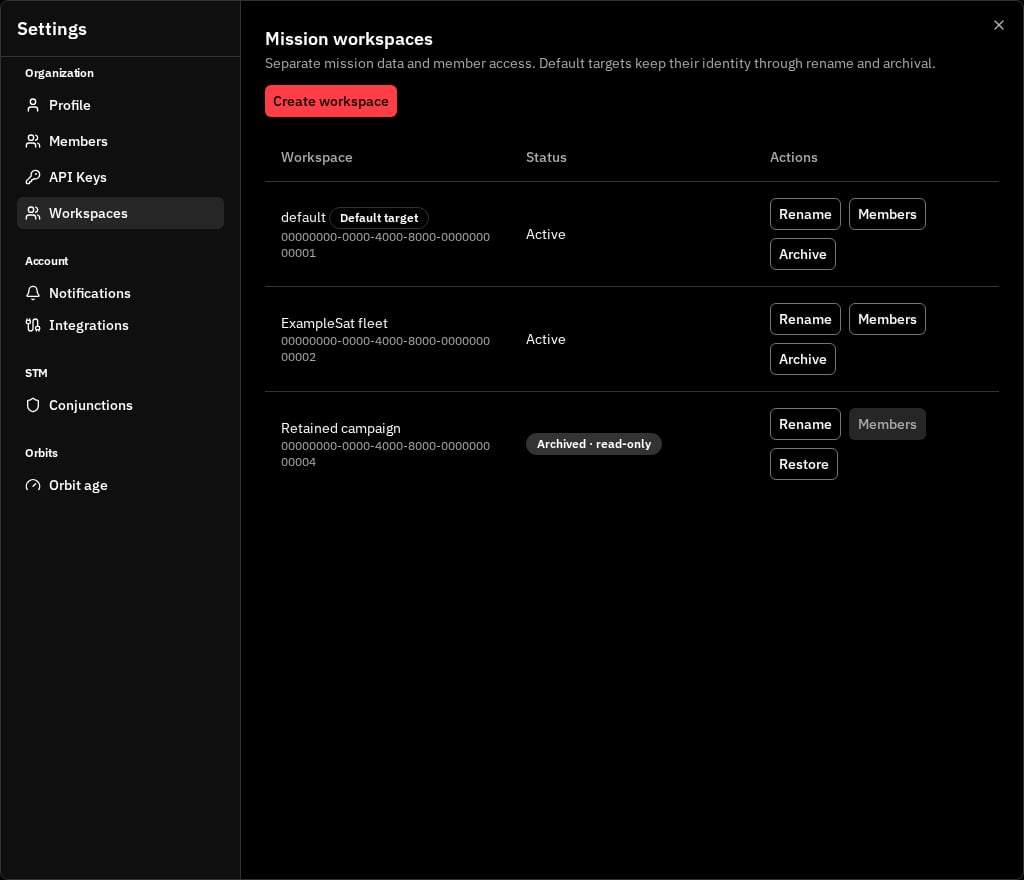
Your organization has a permanent default workspace, initially nameddefault. Existing mission data stays in that default. You can
rename it—for example, to ExampleSat fleet—but its identity stays the
same. Its Default target badge identifies it even after a rename. Renaming or
archiving it does not appoint a replacement default.
Your remembered selection is simply the workspace your browser last opened
for that organization. Selecting another workspace changes what you see;
it does not change the permanent default or where an integration sends requests.
Before you start
- To manage workspaces: you must be an organization administrator, and workspace management must be available for your account or organization. Access to VALAR’s staff administration tools does not by itself make you an organization administrator.
- To use a workspace: an administrator must assign you as a member. Being an administrator or creating a workspace does not automatically grant access to its contents.
- Workspace membership does not enable additional product capabilities or grant extra product permissions.
Create a workspace
- Open Settings from the left sidebar.
- Under the Organization heading, select Workspaces.
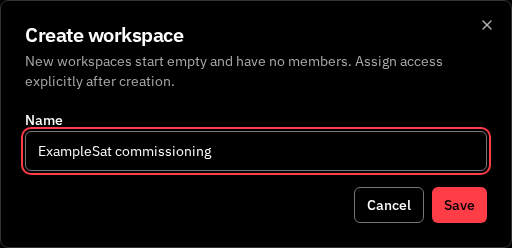
- Click Create workspace.
- Enter a recognizable Name, such as
ExampleSat commissioning. - Click Save. The workspace appears in the administration list.
Assign or remove workspace members
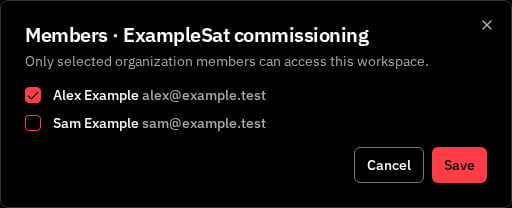
- In Settings → Workspaces, find the workspace’s row and click Members.
- Check the organization members who should have access. Include yourself if you want to work in this workspace. Uncheck a member to remove their access.
- Click Save to apply the membership list.
Member access and permissions
Workspace membership controls where you can work. Your existing product permissions control what you can do there: reading, editing, deleting and approving are still subject to the corresponding resource permissions. Adding a member is not a read-only invitation and does not itself grant every action. There are no per-workspace reader/editor roles. For example, if Alex has spacecraft read and write permissions and belongs to two active workspaces, those permissions apply in both. You cannot use workspace membership to make Alex read-only in one and an editor in the other. An archived workspace is read-only for everyone who retains access. Organization administrators manage workspaces and membership, but still need membership to open a workspace’s mission data. See Authentication and Permissions for resource permission scopes.Select and reopen a workspace
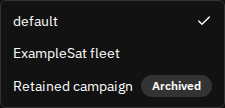
- Open the workspace selector at the top of the left sidebar.
- Choose the entry with the intended name. The check mark identifies the selected workspace; archived entries are labelled Archived.
- Create, import or view mission data in that workspace using its existing workflows.
- A link with
?workspace=<workspace-uuid>selects that workspace. - Otherwise, it reopens your browser’s remembered selection for the organization.
- With neither a link nor a remembered selection, it tries the permanent default, subject to your access.
Reuse work in another workspace
There is no direct move, copy or promote action for transferring spacecraft, plans or other records between workspaces. Select the destination workspace, create its spacecraft and configuration, and set up the plan there. Switching workspaces does not transfer a plan. Individual file workflows can help only where the source offers an export and the destination supports importing that data and format. For example, State Vectors supports OPM export and import: register the spacecraft in the destination first, then import a compatible OPM against that spacecraft. This creates destination data; it does not move the source record or transfer its related configuration, jobs or result history. It is not a general spacecraft or flight-plan migration tool. The same limits apply to existing data in a default workspace. Creating or renaming another workspace does not redistribute that data. Recreate the setup you need in the destination, using supported imports where available, and keep the original workspace for its retained history.Rename, archive and restore
Organization administrators use the actions on each row in Settings → Workspaces.Rename a workspace
Click Rename, enter the new name and click Save. Renaming changes only the display name: the workspace ID, data, membership and integration targets stay the same. You can rename a permanent default too. Its Default target badge and identity stay the same; see The permanent default versus your remembered selection.Archive a workspace
- Click Archive on the workspace’s row and read the confirmation.
- Confirm with Archive. If activity blocks the change, use the listed blocker types and identifiers to resolve it through the existing job, schedule or integration controls, then try again.
Restore a workspace
Click Restore on an archived workspace’s row, then confirm. The same workspace, data and membership become available for normal use again. Previously disabled schedules and disconnected integrations do not restart automatically; enable or reconnect them deliberately through their existing controls. Copying a workspace and permanently deleting it are not supported. Stations remain workspace-specific, as described in the data table above.Troubleshoot workspace access
After an administrator changes your role or access, refresh the app before checking
again. Use Support in the left sidebar if the expected controls remain unavailable.
Connect integrations to a workspace
Provider connections in the application
- Select the target workspace in the sidebar selector and check its name.
- Open Settings → Integrations and configure the available provider using its connection controls. You need the relevant administration permissions.
- Configure any required spacecraft mappings for that workspace. For KSAT, see Importing KSAT antennas.
Your own application or script using the customer API
- Find the workspace UUID. An organization administrator can open Settings → Organization → Workspaces; the UUID is displayed beneath each workspace name. Ask your administrator for it if you cannot open that page. Use the UUID, not the display name.
- Confirm the API key’s access. Manage keys in Settings → API Keys. A key must belong to the same organization and have explicit access to the additional workspace. Your personal workspace membership does not grant access to your API key.
- Arrange additional workspace access before sending requests. There is currently no API-key workspace-grant control in the UI. Ask your organization administrator to coordinate the grant with VALAR support; do not send your secret key. Selecting a workspace in the browser or creating a key while viewing it does not grant that key access to it.
- Send the UUID on requests using
X-Workspace-Id, as below. The header selects a target; it does not grant access.
Application administration endpoints (organization administrators)
Application administration endpoints (organization administrators)
These are the application’s organization-admin JWT operations, not additional
public customer API operations available through an API key. They remain subject
to organization authorization and workspace-management availability. The discovery
endpoint returns only the signed-in member’s authorized workspaces.
Archive blockers return HTTP
409 in the standard error envelope; optional
details.blockers identifies the running jobs or enabled schedules to resolve.Revoking a grant does not change the implicit default binding.